Key Features
Automated Forensics
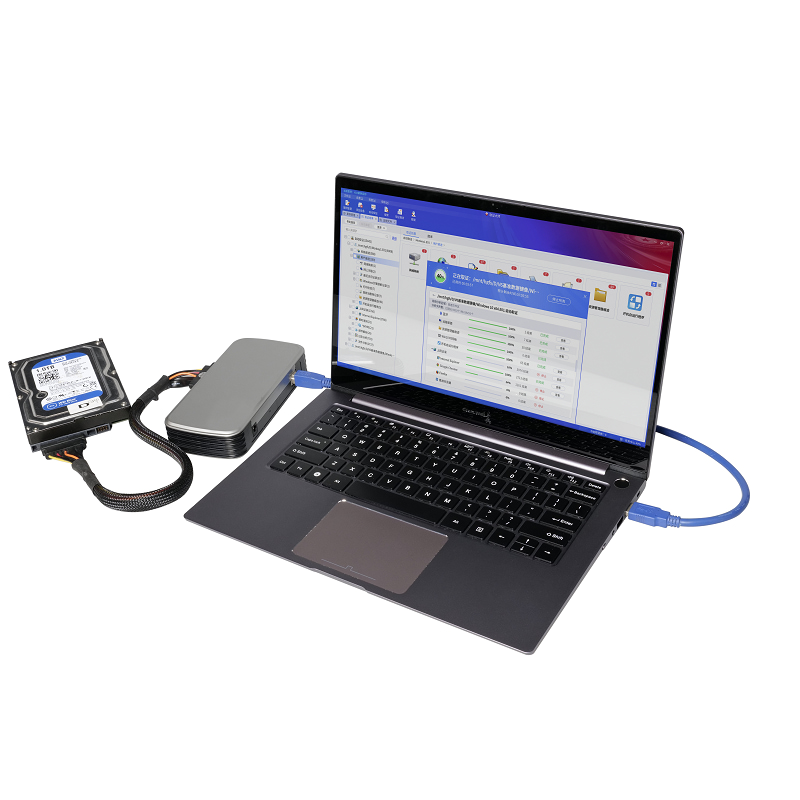
Automates artifact acquisition, residual artifact sorting and classification to streamline case processing from initial evidence capture.
Universal Evidence Access
Supports an extensive library of disks, file systems, forensic images and operating systems, including Windows, macOS and Linux.
Parallel Processing
Captures multiple disks, devices, or forensic images simultaneously to maximize processing throughput and operational efficiency.
Flexible Strategies
Custom extraction profiles enable targeted identification of high-priority forensic artifacts.
Intuitive Interface
A clean, user-friendly design streamlines forensic workflows so officers can focus on the investigation.
Advanced File Analysis
Quickly identifies encrypted objects, spoofed file extensions and anti-forensic traces to reveal concealed evidentiary data.
Why Choose iFM-2008 Forensics Master
● Automated forensics: acquisition to report..
● Universal access: disks, images, Windows/macOS/Linux.
● Multi-source parallel processing.
● Flexible strategies: custom extraction rules.
● Intuitive: built for frontline officers.
● Advanced detection: encrypted & anti-forensic artifacts.